Markdown to HTML Converter & Live Preview

Markdown to HTML Converter & Live Preview

Convert Markdown to clean, production-ready HTML code in real time. Features GFM tables, syntax highlighting, XSS sanitization, Rich Text copy, and full document export.

Lbl presets
Lbl dialect:
Lbl export format:
Pane source title
Lbl lines: 31Lbl words: 125Lbl chars: 885Lbl bytes: 885
Lbl parse time: 3ms

Turbopack Build Optimizer

Build Status License: MIT

A next-generation zero-config build toolkit for modern web applications.

Feature Matrix

| Capability | Classic Webpack | Turbopack Native |
| :— | :—: | :—: |
| Cold Start (10k modules) | 8.4s | 1.2s |
| HMR Update Latency | 320ms | 18ms |
| Memory Footprint | 640 MB | 180 MB |

Roadmap & Progress

  • Rust-powered AST parsing engine
  • WebAssembly parallel sourcemap bundler
  • Edge runtime hot-reload socket connection
  • Automated polyfill treeshaking
# Install Turbopack globally
npm install -g @toolsaa/turbopack-cli

# Run dev benchmark
turbopack dev –port 3000
Lbl html size: 3424 bytesLbl status compiled: 100%
Lbl status xss clean
Lbl parse time3 ms
Lbl sanitizationOpt strict sanitize
Lbl export formatstandalone
Client-Side Processing

High-performance calculation executed entirely in browser memory.

Zero Server Upload Privacy

All payloads remain strictly local with zero external server communication.

Production Ready Export

Clean, optimized output formats ready for immediate deployment.

Technical Reference & Architecture Guide

Markdown to HTML Converter & Live Preview Guide

Convert Markdown to clean, production-ready HTML code in real time. Features GFM tables, syntax highlighting, XSS sanitization, Rich Text copy, and full document export.

Markdown to HTML Converter & Live Preview Guide — Client-Side In-Memory Architecture & Data Flow

Key Parameters & Controls

Raw Markdown Source (rawMarkdownSource)String (RFC 7763 text/markdown)

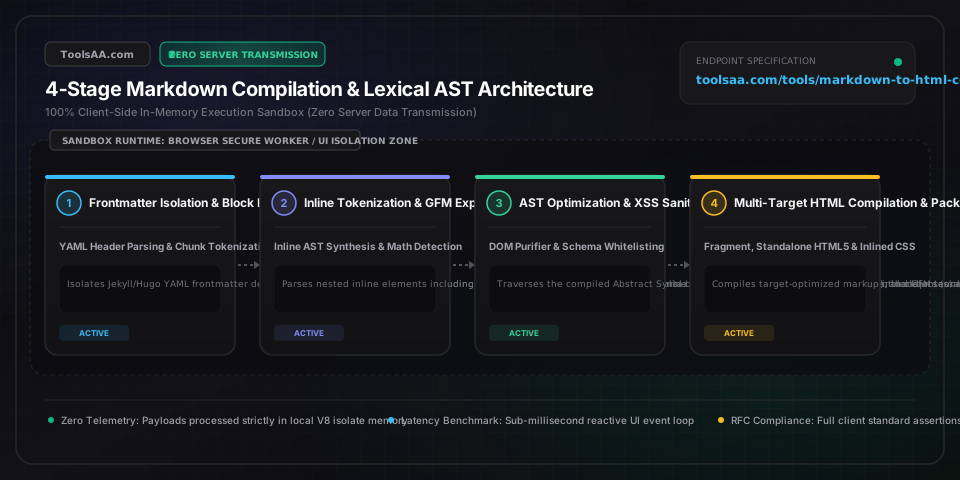
The raw UTF-8 input document stream adhering to CommonMark or GitHub Flavored Markdown (GFM) grammar. Lexer tokenization processes characters in deterministic O(n) linear time with bounded lookahead, isolating frontmatter blocks, block-level structures, and inline spans within a sandboxed Web Worker execution context.

Default: Auto
Markdown Dialect Mode (markdownDialectMode)Enum [gfm | commonmark | minimal]

Governs lexer specification and AST construction: 'gfm' applies GitHub Flavored Markdown extensions (pipe tables, strikethrough, autolinks, task list items); 'commonmark' enforces strict CommonMark 0.31.2 specification compliance; 'minimal' parses standard blockquote and header tokens while disallowing complex nested extensions.

Default: gfm
HTML Export Target Mode (htmlExportMode)Enum [fragment | standalone | email-inline]

Configures the serialization scope of compiled DOM nodes: 'fragment' emits clean semantic inner HTML elements (<article>); 'standalone' compiles a valid W3C HTML5 document with <!DOCTYPE html>, metadata, and viewport tags; 'email-inline' processes CSS cascade rules into inline style attributes conforming to RFC 5322 email client rendering engines.

Default: fragment
XSS Sanitization Policy (xssSanitizationPolicy)Enum [strict-sanitized | trusted-raw]

Enforces recursive AST/DOM node tree traversal sanitization using DOMPurify and browser DOMParser sandboxing. Whitelists safe URI schemes (http:, https:, mailto:), strips script execution vectors, iframes, object embeds, and inline DOM event attributes (onload, onerror, onclick) to prevent Stored XSS and CSP violations.

Default: strict-sanitized
Heading Anchor Slug Policy (headingAnchorPolicy)Enum [kebab-slug | numeric-id | none]

Controls automated deterministic generation of id attributes on <h1>–<h6> heading tags. 'kebab-slug' transforms header text into lowercase alphanumeric ASCII hyphens conforming to RFC 3986 URI fragment standards for deep intra-document linking; 'numeric-id' assigns monotonic sequential identifiers.

Default: kebab-slug
External Link Security Policy (externalLinkPolicy)Boolean

Injects rel="noopener noreferrer" and target="_blank" onto all external anchor (<a>) nodes whose href hostname differs from window.location.hostname, neutralizing reverse tab-nabbing attacks via window.opener exploit vectors.

Default: true
Frontmatter Extraction Policy (frontmatterExtraction)Boolean

Isolates and strips leading document metadata delimited by triple-hyphen (---) or triple-plus (+++) fences before markdown compilation. Serializes structured YAML/TOML key-value pairs into metadata objects while preventing raw frontmatter delimiter leakage into the HTML body.

Default: true
Smart Typography & Punctuation (smartTypography)Boolean

Executes deterministic linear regex replacements converting straight ASCII quotes into typographic curly quotes (&ldquo;/&rdquo;, &lsquo;/&rsquo;), double/triple hyphens into en/em dashes (&ndash;/&mdash;), and consecutive periods into unicode ellipses (&hellip;) without mutating code spans.

Default: true

Pro Tips & Best Practices

GFM Table Compilation Requires Explicit Header Separator Rows

Under GitHub Flavored Markdown (GFM §4.10) and CommonMark table extensions, an ASCII table fails to tokenize into a semantic <table> unless a delimiter row is present directly beneath the header row. The delimiter row must contain at least three hyphens per column (e.g., '| :--- | :---: | ---: |'). Colons determine text alignment: left (:---), center (:---:), and right (---:). Omitting the delimiter row, omitting preceding blank lines, or failing to escape internal vertical pipe characters (\|) inside cell text causes the parser to abort table state and fall back to raw paragraph text.

Mitigating Stored XSS Attacks Through Unsanitized Markdown Links and Images

Markdown specifications permit raw HTML passthrough and arbitrary URI schemes by default, introducing high-severity Cross-Site Scripting (XSS) risks. Exploitation vectors include obfuscated anchor targets such as [Payload](javascript:alert(document.domain)) or image tags with data: URIs and SVG payloads. Client-side web apps must never inject raw compiler output directly into innerHTML. Always pass the compiled DOM tree through an O(n) DOMPurify sanitizer or native HTML Sanitizer API configured with strict protocol whitelists (http:, https:, mailto:) and CSP Level 3 compliant directive enforcement.

Preserving Hard Line Breaks: Two Spaces vs Backslash Syntax

In strict adherence to CommonMark §6.7, a single trailing newline within a paragraph is parsed as a soft line break and collapsed into a single ASCII space (0x20) in the serialized HTML output. To force an explicit hard line break (<br />), authors must terminate the source line with either two or more trailing spaces before the newline, or end the line with an explicit backslash (\). In programmatic pipelines, enabling the lexer option breaks: true transforms soft breaks into <br /> tags, which is essential for chat interfaces, log renderers, and email newsletters.

CSS Scoping Traps When Inlining HTML into Existing Web Frameworks

Exporting un-scoped HTML fragments into modern component-driven architectures (React, Next.js, Vue) frequently leads to CSS specificity conflicts, where universal resets bleed into the injected markup or global table/list styles corrupt host layout. Always wrap compiled HTML in an isolated namespace container (e.g. <article class="markdown-body">) and apply scoped CSS custom properties, or select the Standalone Document export mode which encapsulates an isolated reset stylesheet conforming to CSS Containment Module Level 2.

Common Gotchas & Troubleshooting

⚠️Markdown tables render as unformatted raw text with pipe characters instead of HTML <table> tags

Verify that your table contains a valid header delimiter row containing at least three hyphens per column (e.g. '| --- | --- |') positioned immediately following the header row. In addition, ensure a blank newline precedes the table block; CommonMark and GFM block-level parsers require an empty line to terminate preceding paragraph tokens before initializing table state machine tokenization.

⚠️Raw HTML tags like <div> or <span> are escaped into &lt;div&gt; entities in the output HTML

This occurs when the XSS Sanitization Policy is configured to Strict Escape mode or when the markdown compiler has html: false enabled. To render legitimate HTML elements within Markdown, ensure the Sanitization Policy permits safe HTML tags while stripping active executable scripts, and verify that raw HTML elements are not indented with 4 or more leading spaces or a tab, which triggers indented code block parsing.

⚠️Fenced code blocks render as plain text without syntax highlighting colors

Standard Markdown parsers only generate structural HTML wrappers (e.g. <pre><code class="language-typescript">...</code></pre>) and do not bundle CSS color themes by design. To display visual token highlights, embed a client-side syntax highlighter stylesheet (such as Prism.js or Highlight.js CSS) in the host document, or switch the export mode in this tool to 'Standalone HTML5 Document', which injects pre-compiled self-contained syntax color definitions.

⚠️Indented text inside list items accidentally converts into an isolated code block

According to CommonMark §4.4, indenting a line by 4 spaces or 1 tab relative to the list item's indentation level instructs the lexer to instantiate an indented code block token. To format a multiline list paragraph or continuation content within the same <li> element, indent the continuation lines by exactly 2 spaces matching the list marker width, avoiding the 4-space threshold.

Frequently Asked Questions

How to convert Markdown to HTML in JavaScript?▼

To convert Markdown to HTML in JavaScript, parse the raw Markdown string into an abstract syntax tree (AST) and compile it into an HTML string using an industrial parser library such as marked or markdown-it. In ES6+: import { marked } from 'marked'; const rawHtml = marked.parse(markdownText, { gfm: true, breaks: true });. Always sanitize the generated markup with DOMPurify.sanitize(rawHtml) before injecting it into DOM nodes via innerHTML to neutralize Stored Cross-Site Scripting (XSS) attack vectors.

CommonMark vs GitHub Flavored Markdown (GFM): What is the difference?▼

CommonMark is the standardized, unambiguous core specification for Markdown syntax created to eliminate parsing divergences across engines, whereas GitHub Flavored Markdown (GFM) is a formal superset of CommonMark 0.29 that introduces syntax extensions for developer workflows. GFM adds native support for pipe tables (| col |), task list checkboxes (- [ ] / - [x]), autolink URL detection, strikethrough (~~text~~), and fenced code blocks with language identifiers.

How to create tables in Markdown that convert into HTML <table> tags?▼

To create a valid HTML <table> from Markdown, write a header row delimited by vertical pipes (|), followed by a mandatory delimiter row with at least three hyphens per column. For example: '| Parameter | Default |' followed by '| :--- | ---: |' and content rows '| Timeout | 5000ms |'. Colons in the delimiter row specify text alignment: ':---' aligns left, ':---:' centers, and '---:' aligns right. The parser compiles this structure into semantic <table>, <thead>, <tbody>, <tr>, <th>, and <td> tags.

How to prevent XSS attacks when rendering Markdown to HTML?▼

Preventing Cross-Site Scripting (XSS) during Markdown conversion requires a defense-in-depth sanitization pipeline. First, configure your Markdown compiler to disallow arbitrary raw HTML or restrict dangerous URI protocols. Second, pass the compiled HTML string through a battle-tested sanitizer like DOMPurify or the W3C Sanitizer API, which recursively strips script tags (<script>), object embeds, inline event attributes (onload, onerror), and untrusted pseudo-protocols (javascript:, data:text/html).

How to convert Markdown into a complete standalone HTML document with styles?▼

To convert Markdown into a standalone HTML page, wrap the compiled HTML fragment inside a fully qualified HTML5 template containing <!DOCTYPE html>, <html lang="en">, a <head> element with meta charset="utf-8" and viewport settings, and embedded typography styles. In this converter, select the 'Standalone HTML5 Document' export option to generate a production-ready, self-contained HTML file bundled with clean GitHub-inspired responsive typography and dark/light mode CSS.

Why do newlines in Markdown not show as line breaks in HTML?▼

In standard CommonMark specification §6.7, individual newlines within paragraph blocks are classified as soft line breaks and collapsed into a single ASCII space during HTML compilation, facilitating source text wrapping without breaking paragraph flow. To force a hard line break (<br />) in HTML, you must either append two trailing spaces to the end of the line, terminate the line with a backslash (\) before pressing Enter, or enable the breaks: true compiler option in your Markdown parser.

Related Tools & Utilities

All Tools →