Card config title
Badge csprng
Lbl range min
Lbl range max
10
Lbl unique drawLbl unique draw desc
Lbl precision decimalsLbl precision decimals desc
Card title sequence(0 Lbl observations)
Hero subheadline
High-performance cryptographic and seeded random number generator. Generate true random integers, decimals, Gaussian distributions, and lottery draws with real-time chi-square uniformity telemetry and instant export.
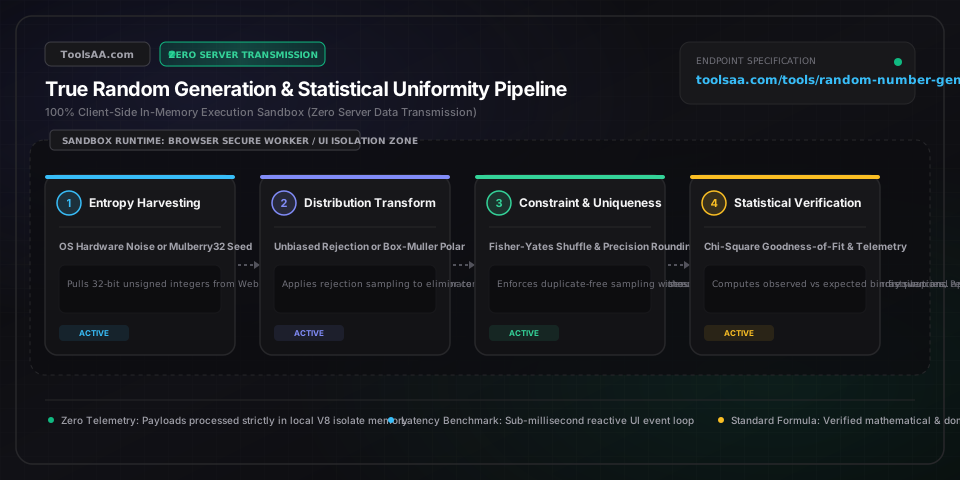
Inclusive closed interval [a, b] bounding all generated values. Supports 64-bit safe integers up to +/- 9,007,199,254,740,991.
Total quantity of random numbers generated per execution batch. Supports 1 to 10,000 items with zero main-thread UI freeze.
Selects between cryptographically unguessable hardware entropy (window.crypto) and deterministic seed-reproducible pseudo-randomness.
Governs probability density: Uniform assigns equal likelihood; Gaussian uses Box-Muller polar transform; Exponential models Poisson arrival intervals.
When unique mode is enabled, Fisher-Yates partial reservoir sampling guarantees no duplicate items, requiring Count <= Max - Min + 1.
Standard beginner implementations compute random ranges using Math.floor(rng() * (max - min + 1)) or raw modulo operations (random % range). When the entropy range is not an exact integer multiple of the target range, lower numbers receive an unfair probability bump (modulo bias). This tool enforces rejection sampling on raw 32-bit uints to guarantee mathematically uniform probability across every value.
V8 and modern JavaScript engines implement Math.random() using xorshift128+, an algorithm optimized for speed rather than security. After observing merely 2 to 3 consecutive internal 64-bit float outputs, the entire internal 128-bit state can be reconstructed using Z3 SMT solvers, enabling attackers to predict all future values. Always utilize the CSPRNG engine for raffles, token generation, cryptography, and lotteries.
Generating continuous bell-curve distributions requires transforming pairs of independent uniform random variables U1, U2 in (0, 1) into standard normal deviates: Z0 = sqrt(-2 * ln(U1)) * cos(2 * pi * U2). Our engine computes this transform with double precision and scales by mu + Z0 * sigma, avoiding the Central Limit Theorem crude 12-dice summation approximation.
When Uniqueness (sampling without replacement) is enabled, the pigeonhole principle mandates that Count N cannot exceed (Max - Min + 1). For example, picking 60 unique numbers between 1 and 50 is mathematically impossible. Either broaden the [Min, Max] interval, reduce the Count, or toggle off Uniqueness to allow replacement.
The Pearson Chi-Square test asymptotically follows a chi-squared distribution only when the expected frequency in each discrete bin satisfies E_i >= 5. When testing small batches (e.g. N = 20 across 10 bins, where E_i = 2), random Poisson variance will naturally produce extreme p-values. For statistically rigorous uniformity verification, generate at least 500 to 1,000 samples.
To generate random numbers without duplicates, the generator uses sampling without replacement via the Fisher-Yates shuffle algorithm. Starting with an array of values from Min to Max, the algorithm iteratively selects a cryptographically secure random index and swaps it with the current position, extracting N unique values in O(N) linear time while ensuring every permutation is equally probable.
A Pseudo-Random Number Generator (PRNG) uses a mathematical recurrence formula starting from an initial seed. If the seed is known, the entire sequence is 100% deterministic and predictable. A Cryptographically Secure PRNG (CSPRNG), such as window.crypto.getRandomValues, harvests unpredictable physical entropy from operating system hardware interrupts and thermal noise, satisfying the next-bit test where no polynomial-time algorithm can predict subsequent bits.
Our generator applies the Box-Muller transform to map two uniformly distributed independent random values into two standard normal random variables with mean 0 and variance 1. The result is then scaled by X = mu + Z * sigma, allowing you to model real-world phenomena such as measurement errors, IQ distributions, financial returns, and biological metrics.
The Chi-Square Goodness-of-Fit test divides the range [Min, Max] into k equal bins and computes the statistic chi2 = sum((Observed - Expected)^2 / Expected), where Expected = N / k. By comparing the calculated chi2 against the chi-square distribution with k - 1 degrees of freedom, the tool computes a p-value: a p-value between 0.05 and 0.95 confirms that the observed distribution is consistent with true theoretical randomness.
Math.random() is neither cryptographically secure nor seedable in standard browsers. Its internal PRNG algorithm (xorshift128+ in V8/Chrome and PCG in WebKit/Safari) has a small internal state space that can be fully deduced after observing a short sequence of numbers, making it vulnerable to reverse-engineering in lotteries, gambling, token generation, or cryptographic operations.
Free client-side developer and designer tool.
Free client-side developer and designer tool.
Generate custom WiFi QR codes instantly with real-time vector preview. Supports WPA3, WPA2, WEP, and hidden networks. Download high-res SVG, PNG, or print guest signs and table tents.
Instant VAT calculator to add or remove value added tax. Calculate gross, net price, and tax breakdown across UK, EU, and global standard or reduced VAT rates.
Calculate your TDEE and daily maintenance calories with precision. Compare Mifflin-St Jeor, Katch-McArdle & macro splits for weight loss, cutting, or bulking.
Calculate sample and population standard deviation, variance, mean, and margin of error instantly. Clean messy datasets with outlier detection and normal curve.